About

Cybersecurity and regulatory compliance with one expert team

Dyasol is a consultancy registered in Bulgaria, working with clients in the EU and beyond. We combine cybersecurity, regulatory compliance, technology and business psychology, and a designated specialist is accountable for every engagement.

How we work

  1. Understand the needWe discuss the trigger, the deadline and the information you already have.
  2. Agree the scopeWe define the tasks, the deliverables and the client input required, and fix them in writing.
  3. Deliver the workWe carry out the agreed tasks and discuss the gaps we identify as we go.
  4. Review the resultsWe present the findings, their limitations and the next actions, and agree whether a further step would be useful.
The four steps as we work them, in order.
  • A fixed price for a scope we confirm in writing before we start — no hourly billing on packaged work.
  • A written quote within two business days of receiving the information needed.
  • The payment schedule is stated in the written quote; you have 10 working days to review the deliverable and one round of corrections within scope is included.
  • Re-verification of remediated findings where it is part of the agreed scope.
  • 30 days’ notice to cancel monthly subscriptions. Annual programme terms are set out in the proposal.
  • Vendor-neutral — we receive no commissions from technology vendors. Where a referral partner introduced you, that relationship is disclosed to you.

We prepare and deliver improvements; independent audit and certification are commissioned separately.

The team

Dyasol works with a core team and a long-standing network of specialists selected for each project. We combine experience in GRC, cybersecurity, development, DevOps, AI, IT management, project management and business psychology. Before an engagement begins, the client receives information about the engagement lead, the participating specialists and their roles. Some expert profiles are presented publicly by area of expertise.

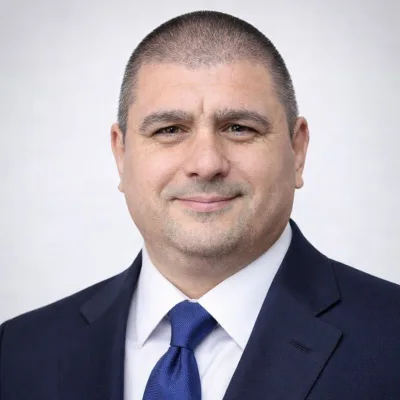
Angel Brenishki

Angel Brenishki

Managing director — Cyber Security, Governance, Risk and Compliance lead

Sets the scope and the technical direction of the work.

Angel brings 28 years of experience in technology and cybersecurity, from systems development and critical infrastructure protection to leading security and ICT (information and communication technology) risk management in international financial organisations. He holds a PhD in Cybersecurity from the University of Ruse “Angel Kanchev” and has taught in a cybersecurity management master’s programme at the University of National and World Economy in Sofia.

His experience includes risk assessment, audit preparation and work on DORA (EU Digital Operational Resilience Act), NIS2 (EU cybersecurity directive) and ISO 27001, alongside hands-on design and implementation of technical safeguards. He has worked on access management, threat detection, penetration testing and remediation of identified weaknesses, followed by verification.

For Dyasol clients, this experience connects organisational requirements with the actual state of their systems and the implementation of suitable improvements.

Qualifications: Certified Chief Information Security Officer (Executive) and Certified in Governance, Risk and Compliance (GRC); specialised training in ISO 27001, ITIL 4 and AWS and Azure security architecture.

Professional profile on LinkedIn →

Responsibilities
Owns
Scoping, the technical and regulatory direction of the work and the named officer roles. Every deliverable is reviewed by a senior specialist before it leaves Dyasol.
Works alongside
Facilitation and behavioural analysis in human-factors work are led by Diana Ginova; he attends or is reachable throughout and answers any technical question raised.
Languages
Works in Bulgarian and English.
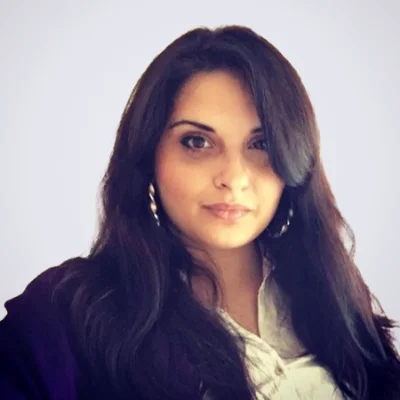
Diana Ginova

Diana Ginova

Partner — business psychology and cyberpsychology

Leads the sessions and the behavioural analysis.

Experience in psychology, psychotherapy, work with corporate clients and occupational burnout. Developing her practice into cyberpsychology.

Responsibilities
Owns
Leading the sessions, behavioural analysis and the human-factors analysis in an engagement: how executives decide under pressure, how manipulation and influence work inside legitimate business threads, and how people actually behave around security and AI rules.
Works alongside
Technical statements, threat scenarios and control recommendations are owned by Angel Brenishki, Dyasol’s security lead. Any technical question raised in a session is logged and receives a first written response within one business day; a full resolution may take longer.
Languages
Works in Bulgarian and English.

Kostadin Mihaylov

Specialist — law, expert examination and dispute resolution

Legal and contract review within the agreed scope.

Kostadin Mihaylov is an attorney registered with the Varna Bar Association, a court-appointed expert and a mediator. He holds a master’s degree in law and a doctoral degree from Nikola Vaptsarov Naval Academy.

He has taught the course “Expert examination of payment systems, cryptocurrencies and blockchain” at Nikola Vaptsarov Naval Academy. He has completed training on the Bulgarian Cybersecurity Act, the minimum network and information security requirements and the changes introduced by NIS2.

Responsibilities
Owns
Legal and contractual review, dispute resolution and expert matters within the agreed scope of an engagement.
Works alongside
Technical assessments, threat scenarios and security-control recommendations are led by the responsible cybersecurity specialist. Legal representation and formal legal opinions are commissioned and described separately when needed.
Languages
Works in Bulgarian and English.
Radoslav Tsvetkov

Radoslav Tsvetkov

Delivery and compliance programmes — deputy engagement lead

Coordinates tasks, deadlines and acceptance.

Radoslav holds a degree in Web Technologies from Edinburgh Napier University. He spent fifteen years in the United Kingdom and has worked with leading technology companies across the UK, Europe and the United States. His career began in web development and moved into project management, delivering technology projects with engineering teams and suppliers.

For the last three years he has focused on government regulation and compliance: turning regulatory requirements into plans with owners and deadlines, and keeping agreed activities on track until they are completed and evidenced.

Responsibilities
Owns
Project planning, delivery coordination and tracking of the compliance activities agreed with the client: milestones, owners, deadlines, client inputs and acceptance. He is the named deputy for engagement contact and coordination, so the client always has a second person who knows the status of the work.
Works alongside
Technical assessments and legal interpretations remain with the responsible cybersecurity and legal specialists, with whom he works alongside.
Languages
Works in Bulgarian and English.

The practical approach of Angel Brenishki, PhD is also set out in his research publications.

Areas of expertise and specialist network
  • Cybersecurity

    Threat scenarios, control design, external exposure, e-mail and domain trust, incident coordination.

  • Regulatory requirements and governance

    DORA, NIS2, the EU AI Act, the GDPR (General Data Protection Regulation) and the frameworks clients are asked to evidence — mapped to what an organisation actually does.

  • Development, DevOps and AI

    Product and cloud architecture, secure development, CI/CD, infrastructure as code, AI integrations and the technical fixes identified by an assessment.

  • IT and project management

    Planning, ownership, dependencies, delivery coordination and controlled implementation across internal teams and suppliers.

  • Business psychology and cyberpsychology

    Methods for addressing occupational burnout and improving the effectiveness of managers and employees; recognising and responding to social-engineering attempts and other malicious actions against the organisation; and designing verification and escalation that hold up under pressure.

Areas of expertise covered by the core team and the specialist network.

Specialists are selected for the capabilities and availability a project needs. Before work starts we agree their roles, the access to information they need and any conflicts of interest, and the specific composition is presented to the client. Relevant professional experience is discussed when assigning the team, without disclosing other confidential engagements.

Accountability, independence and what we are not

Accountability

  • Every engagement has a designated engagement lead who reads every document before it leaves Dyasol and answers for it — to your management, your auditor or your supervisor.
  • We deliver with a core team and a network of specialists selected for each project. Independent certification and any applicable independent audit are commissioned from separate competent bodies, which you contract directly. Where legal advice is required, we agree the involvement of a qualified legal professional. We say so before you engage us.
  • We document scope, findings and limitations. Decisions by regulators, auditors or clients remain theirs to make.

What a company registered in Bulgaria means for regulated work

Dyasol Ltd is registered in Sofia, Bulgaria — inside the European Union. For clients under EU financial and cybersecurity regulation, contracting an EU-established provider simplifies procurement: the outsourcing and third-country questions that a non-EU provider raises do not arise in the same form.

It does not remove your own duties. DORA Article 30(2)(b), for example, requires the contract with any ICT provider to state the regions or countries where services are provided and data is processed, whoever the provider is. For each engagement we therefore agree the applicable requirements for confidentiality, access, subcontractors and data location, and we put them in writing.

Who we work for

We work for organisations that want to meet their obligations and be able to show it. Every new client passes a short, documented acceptance check before the first contract; we decline work for sanctioned entities and for businesses that deceive their clients or regulators.

What we are not.

  • Not a web or marketing agency, and not general IT support.
  • Not a certification body, a statutory auditor or a law firm — those must stay independent of us, and we say so before you engage us.
  • Not a 24/7 incident-response team of our own — we provide round-the-clock response through a vetted partner under a separate contract.
One rule that applies to people as well as systems. Independent certification and statutory audit are done by bodies independent of us; checking that our own fixes work is part of every engagement’s acceptance. In human-factors work we assess situations and decisions, never individuals: no employee is scored, profiled or singled out.

If you are preparing a procurement, see the supplier information.